Security
Security built into every layer
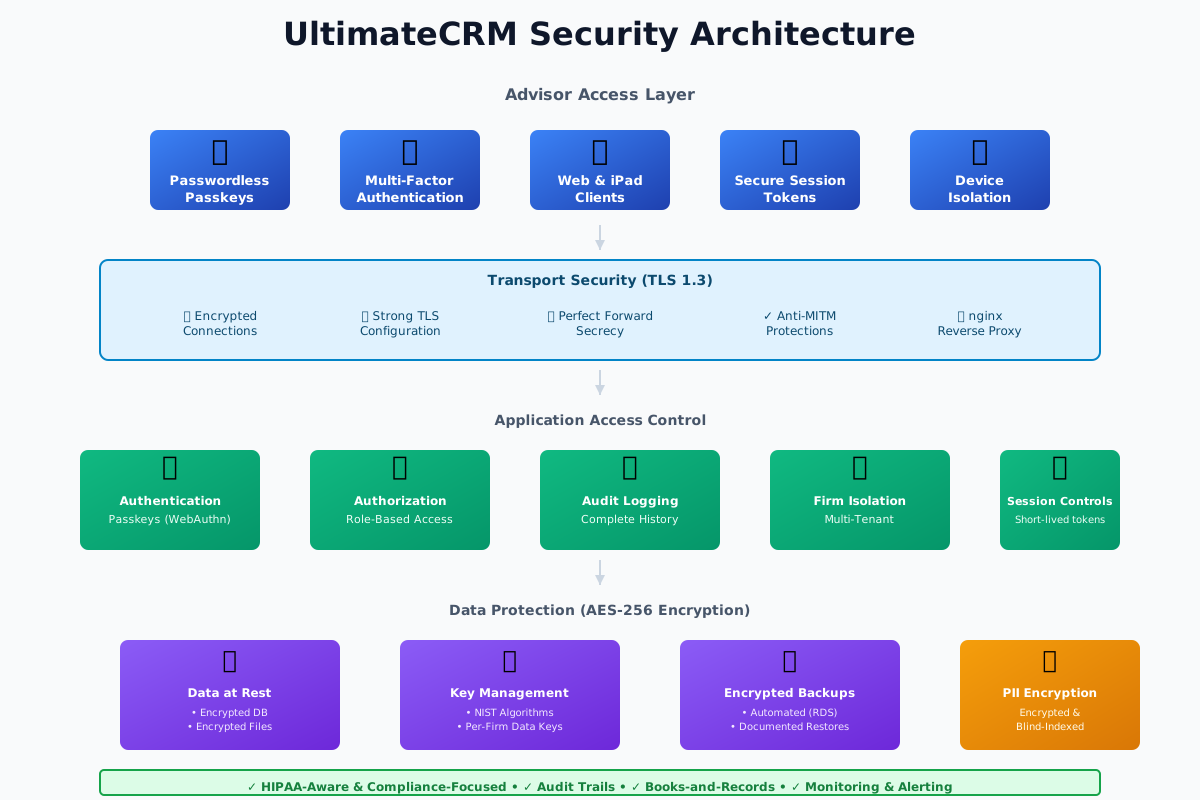
UltimateCRM protects your clients and your firm with AES-256 encryption, TLS 1.3, passwordless passkey sign-in, and tenant isolation enforced in the database itself — and this page describes exactly what we do, in plain language.
AES-256 is the algorithm standardized in FIPS 197, and AES-GCM is a FIPS 140-3 approved mode (NIST SP 800-38D). Both NIST and the NSA (CNSA 2.0) rate AES-256 as resistant to attack by quantum computers.
Engineered for trust
Cryptography you can rely on
We use NIST-approved algorithms and modern key management to protect every connection, file, and stored record. That means AES-256 encryption, TLS 1.3, and secure identity controls throughout the application stack.
- 256-bit encryption for data at rest, across both the database and the file store
- AES-256 as standardized in FIPS 197, used in GCM mode (NIST SP 800-38D) — a FIPS 140-3 approved algorithm and mode
- Rated quantum-resistant by both NIST and the NSA: AES-256 is the symmetric algorithm required by the NSA's CNSA 2.0 suite, and NIST's post-quantum guidance keeps it in place without change
- NIST-approved cipher suites for transport and storage
- Passwordless passkeys and MFA-ready authentication for advisor access
- Firm-specific key isolation so each practice stays logically separated
Protecting client data
Encrypted files, encrypted PII
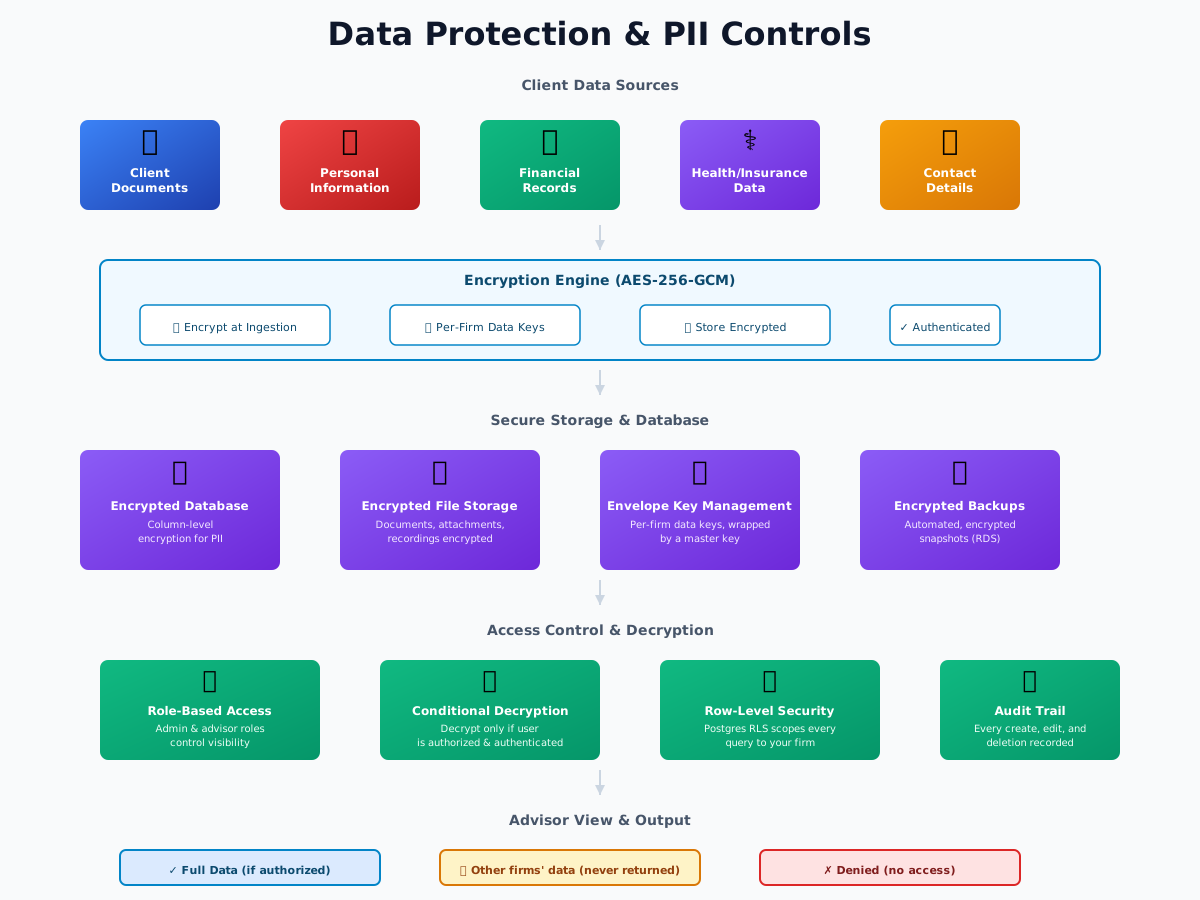
Sensitive client information is never stored in plaintext. Documents, personal identifiers, contact details, and financial attachments are encrypted and accessed only through approved application sessions.
- Encrypted file storage for client documents and attachments
- Sensitive personal fields encrypted before they reach the database — never stored in plaintext
- Tenant isolation enforced in the database with PostgreSQL row-level security
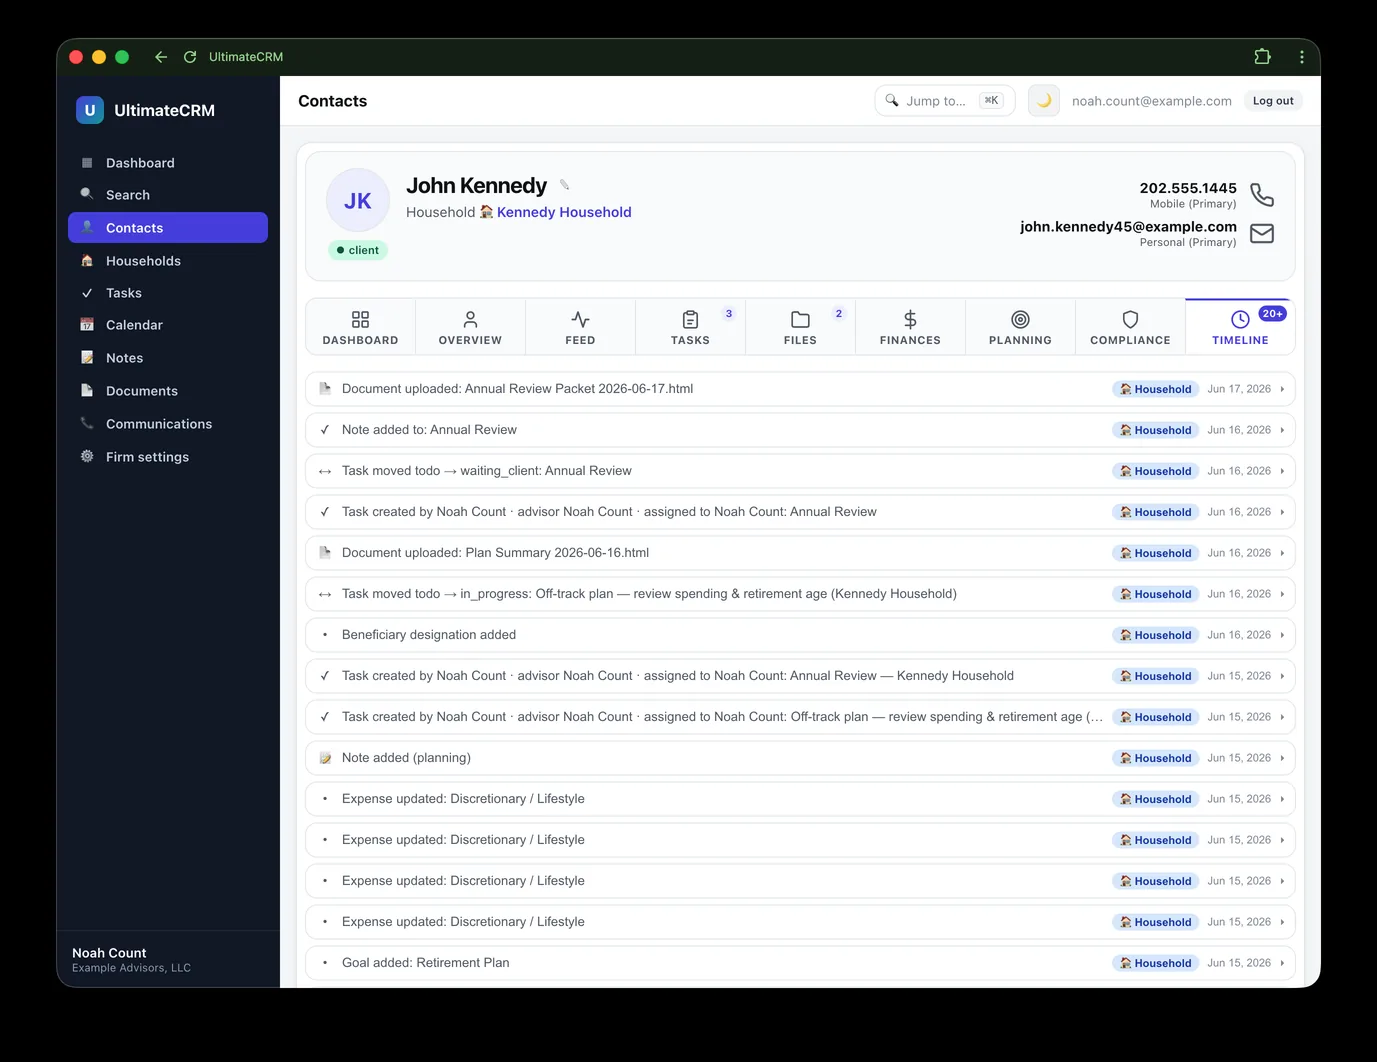
- A complete audit trail of creates, edits, and deletions
Available when you need it
Where your records actually live
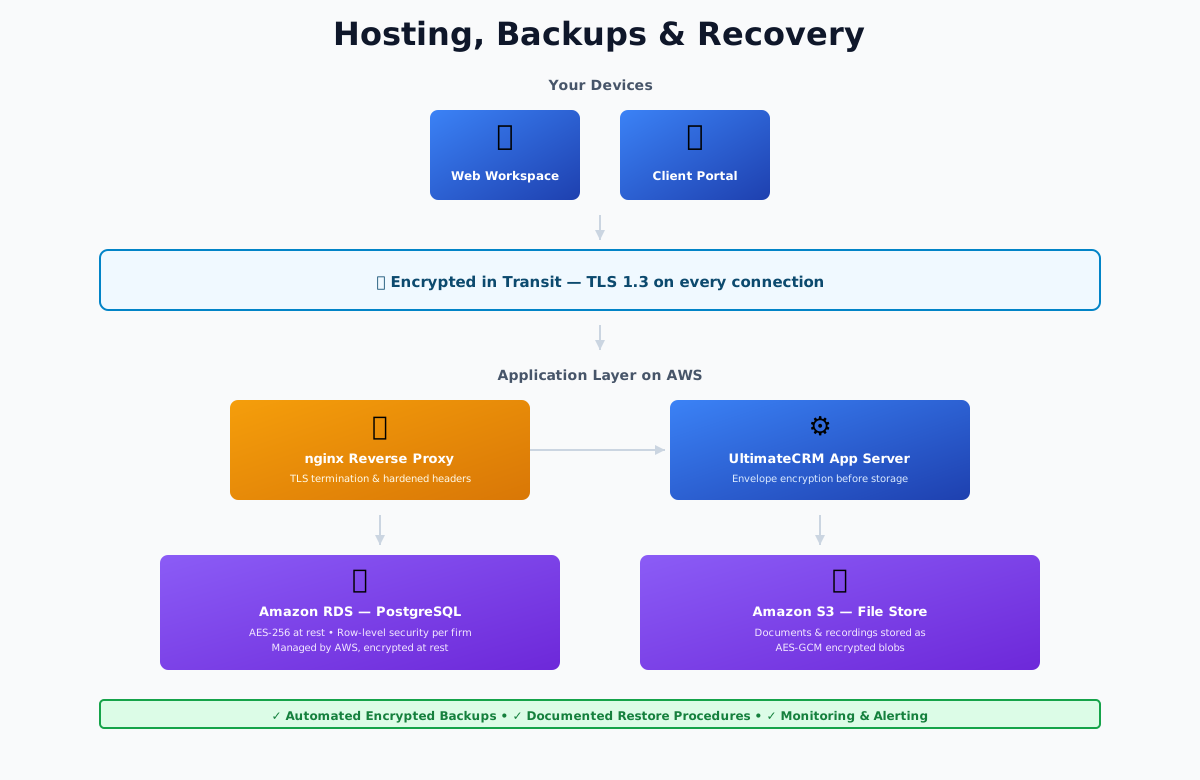
UltimateCRM runs on managed AWS infrastructure: PostgreSQL on Amazon RDS, files on Amazon S3, and TLS terminated at a hardened reverse proxy. Every document is encrypted by the application before it is handed to S3, so the storage layer only ever holds ciphertext.
- Hosted on AWS with managed PostgreSQL on Amazon RDS
- Documents and recordings encrypted by the application before upload to Amazon S3
- TLS 1.3 terminated at a hardened reverse proxy; unknown hosts are refused outright
- Access logs for every request to every host — address, time, path, outcome — kept up to 13 months on our servers and up to 7 years in a write-once archive in our own AWS account; query strings, where sign-in codes travel, are never written to them
- In-app system health reporting that tells your firm when an integration stops delivering records — including the silent case where nothing errors and nothing arrives
We describe our resilience posture in specifics rather than adjectives — and we would rather say less here than imply a control we do not operate. Written answers on backup retention, recovery objectives, and incident response are available to firms in due diligence.
Compliance-ready controls
Built for advisory compliance
Our platform aligns with the security needs of financial advisors and their clients, including HIPAA-aware data handling, audit trails, and firm-level governance.
- HIPAA-aware protection for health-related client information and PII
- Books-and-records support for calls, emails, and document activity
- Firm-wide security policies, including require-passkey MFA for every user
- Sign-in history for your team — every sign-in, failed attempt and lockout, with the address and browser it came from, visible to your firm's administrators in Settings
- Strong passwordless sign-in with passkeys, biometrics, and MFA readiness
Security that lets your firm move faster
UltimateCRM combines modern encryption, data protection, and availability so advisors can focus on clients, not maintenance.